Talk On AccessToken & RefreshToken:
Guide to Secure Authentication
🎟️ Imagine This...
You go to a movie theatre.🙂
You get a ticket to watch a movie. That’s your access token.
But you also have a VIP card in your pocket — if your ticket expires, you flash that card to get a new one. That’s your refresh token.
Boom. 🎬 You just understood token-based authentication.
🧐 So, What Exactly Are These Tokens?
✅What is an Access Token?
🔑 Short-lived token
🕒 Used on every API call
⚠️ If stolen → attacker can act as user (temporarily)
🔁 Refresh Token
Long-lived (like 7 days)
Stored securely (usually in an HTTP-only cookie)
Used only to get a new access token
Must never be exposed to JavaScript
Why Two Tokens?
🔄 Why Two Tokens?
Because security + user experience need balance.
| Feature | Access Token | Refresh Token |
| Used every time? | ✅ Yes | ❌ No |
| Short-lived? | ⏱️ Yes | ⏳ No |
| Safer to expose? | ⚠️ Somewhat | ❌ NEVER |
| Stored in? | Header or cookie | HTTP-only cookie |
| If stolen? | 🔓 Small damage | 🔥 Big damage |
🔍 Wait… What Are These Tokens Made Of?
Both access and refresh tokens are stored in JWT (JSON Web Token) format.
It’s basically a compact string that carries some data (like your user ID), and is cryptographically signed so that it can’t be tampered with.
🧠 A JWT has 3 parts:
header.payload.signatureExample:
  CopyEditeyJhbGciOiJIUzI1NiIsInR5cCI6IkpXVCJ9.
  eyJfaWQiOiIxMjM0NTYiLCJyb2xlIjoidXNlciJ9.
  VZciYXNnNklfdWZlc3Rfc2lnbmF0dXJl
You can decode it at jwt.io to peek inside.
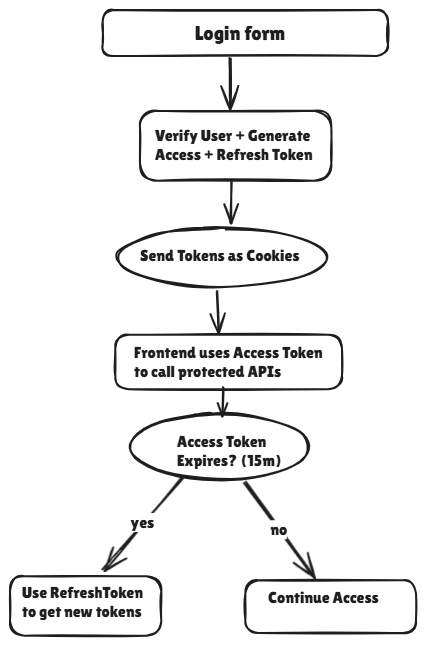
Here’s a workflow:
🔓 What if tokens are exposed?
If someone gets hold of your access token:
They can make API requests on your behalf until it expires.
Risk level: moderate
🛡️ Mitigation: Short token lifespan (e.g., 15 mins)
If someone gets your refresh token:
They can keep generating new access tokens = full account hijack!
Risk level: high
🛡️ Mitigation:Store in
httpOnlycookieRotate tokens on use
Invalidate on logout
🔐 Security Measures You Should Always Use
✅ Store refresh tokens in
httpOnly,securecookies
✅ Rotate refresh tokens after each use
✅ Clear tokens on logout
✅ Validate token against DB before use
✅ Add expiry to both tokens
~Auth tokens are like keys to your kingdom — treat them like secrets, not souvenirs